Let us know how we can help
Sales & Pricing
Speak to a rep about your business needs

Help & Support
See our product support options
General inquiries and locations
Contact us

 Control-M + GCP Managed Instance Group
Your GCP Managed Instance Group workflow starts before a Compute Engine instance group update ever executes — and it can fail when something upstream breaks. A Cloud Storage deployment manifest that never arrives. A Cloud Build release that finishes after the maintenance window. Control-M coordinates these GCP services through their respective Control-M job types; the Managed Instance Group plugin itself handles instance group lifecycle, targeted instance actions, and unmanaged group provisioning.
common workflow issues
Does this sound like your week?
These aren’t edge cases. They’re the normal operating conditions for teams running GCP Managed Instance Group workflows across multiple tools. Here’s how Control‑M handles each one.
DEPLOYMENT DEPENDENCIES
Your Cloud Build release finished late. The 02:00 instance group update already started.
Control-M makes the Managed Instance Group update dependent on successful Cloud Build completion. The update runs only after its prerequisites succeed, preventing premature infrastructure changes and keeping release sequencing consistent across tools.
UPDATE FAILURES
Compute Engine accepted your update request. The rollout still hasn't finished successfully.
Control-M monitors the configured Managed Instance Groups job status, results, and output. Status polling and failure handling expose unsuccessful operations, while job dependencies prevent subsequent workflow stages from proceeding on an unsuccessful Control-M job result.
INSTANCE RECOVERY
A managed VM needs recreation. Your recovery steps span three separate tools.
Control-M schedules the supported instance recreation action within a coordinated workflow, with upstream conditions and downstream verification jobs. Operators can track execution and handle failures centrally instead of manually coordinating recovery across disconnected scripts and consoles.
API RATE LIMITS
A Compute Engine API returns HTTP 429. Your overnight maintenance job fails.
Control-M centralizes job execution and failure handling for instance group operations, so failed overnight maintenance jobs surface immediately and can be rerun from a single console rather than manually restarted.
MAINTENANCE SLA RISK
Your instance group maintenance is running late. The 06:00 service handoff is approaching.
Control-M attaches SLA management to Managed Instance Groups jobs and tracks dependencies across the complete workflow. Teams gain visibility into deadline risk, can escalate delays, and coordinate downstream handoffs against defined service commitments.
Control‑M + GCP Managed Instance Group
Control‑M + GCP Managed Instance Groups
|
API and automation capabilities |
Control-M Automation API · Job:GCP Managed Instance Group · JSON job definitions · Compute Engine REST API · ctm provision image CLI · status polling · configurable API retries · lifecycle actions: create, update, delete, and status monitoring of instance groups; instance-level stop, start, recreate, and apply pending updates; create and delete unmanaged instance groups. |
|
Deployment models & infrastructure flexibility |
Control-M SaaS · Control-M self-managed · Linux Agent · Windows Agent · centralized connection profiles · Google Cloud projects · Google Cloud REST API operations for managed and unmanaged instance groups · Control-M Application Integrator plug-in |
|
Security posture |
Google Cloud service account authentication · IAM-based authentication · centralized credential profiles · Google Cloud IAM permissions · Control-M access controls · secured connection configuration · job execution history |
|
Incident response & MTTR enablement |
job status polling · failure-based dependency control · job output inspection · automated recovery workflows |
end-to-end orchestration
One production workflow. Every tool in the stack.
Control‑M orchestrates workflows across GCP Managed Instance Group, Cloud Build, Cloud Storage, Compute Engine, Cloud Monitoring, and cloud services in a single job flow — with dependency tracking, SLA visibility, and automated recovery across all of them.
- Cross-tool dependency: Cloud Storage artifact → Cloud Build → GCP Managed Instance Groups update → deployment verification
- Data-aware triggers: Cloud Storage file arrival, API event, Cloud Build completion, upstream job result
|
GCP Managed Instance Group |
Create and update groups · control managed instances · monitor job status · coordinate dependencies |
|
Google Cloud Build |
Coordinate build completion · gate infrastructure changes · track upstream job outcome |
|
Google Cloud Storage |
Detect artifact arrival · initiate dependent workflows · coordinate file-based prerequisites |
|
Google Compute Engine |
Coordinate VM operations · sequence infrastructure jobs · manage cross-job dependencies |
|
Google Cloud Monitoring |
Coordinate monitoring checks through configured jobs or APIs · sequence operational verification |
|
Google Cloud Functions |
Execute function jobs · automate verification steps · coordinate downstream actions |
airflow coexistance
Control‑M doesn’t replace your Airflow DAGs. It runs the layer above them.
The objection is common: “We’re already on Airflow.” The issue isn’t what Airflow does – it’s what happens before and after Airflow runs. That’s where pipelines actually fail.
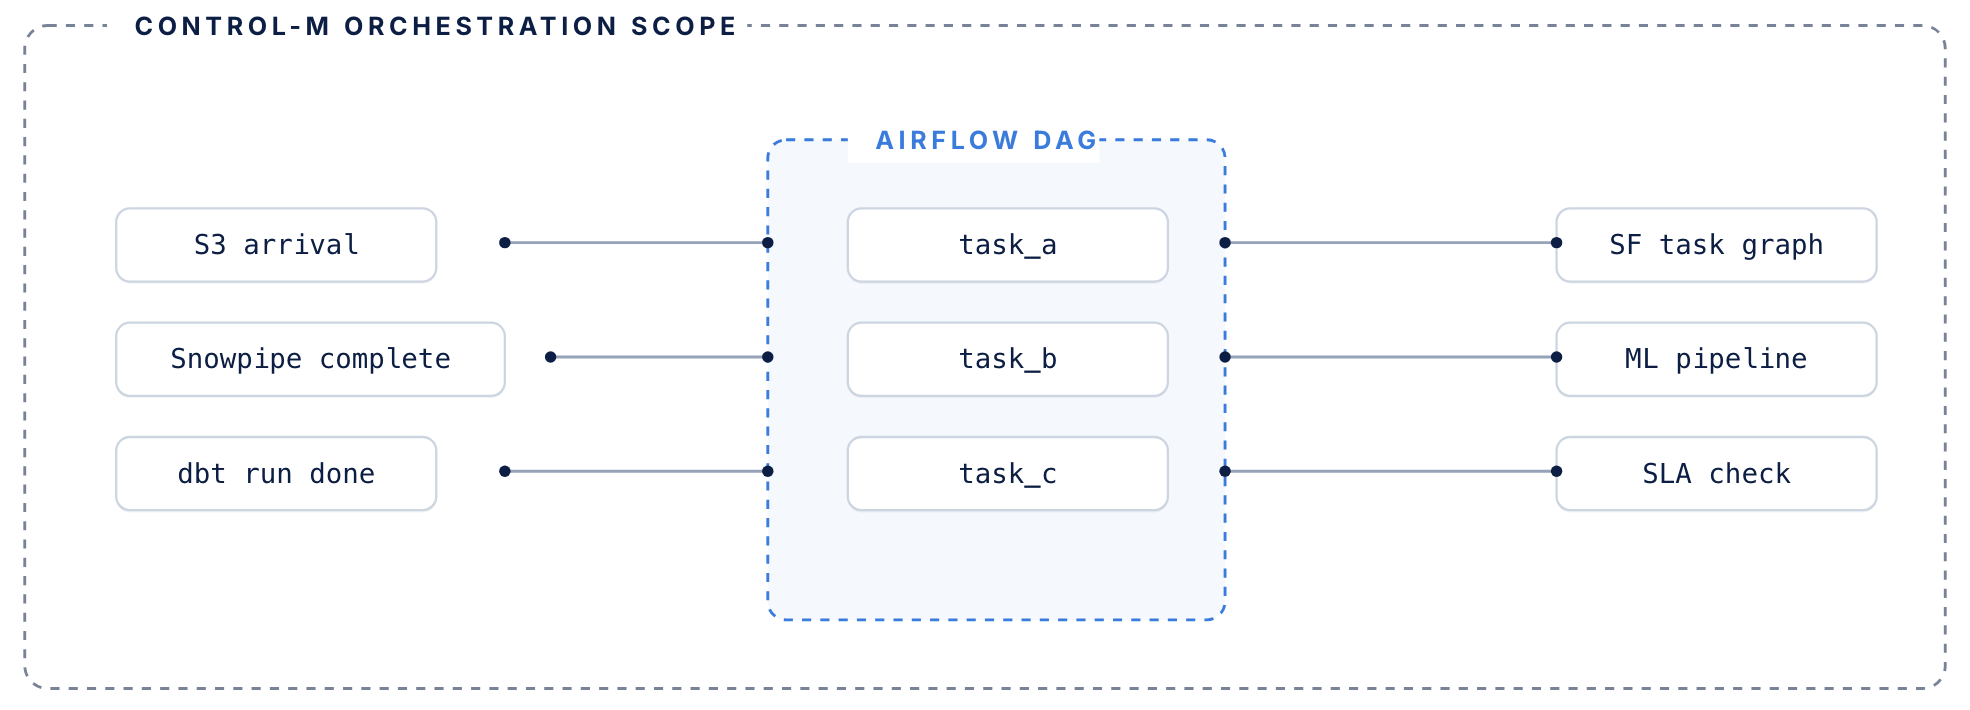
Airflow manages its DAG. Control-M manages everything surrounding it.
airflow handles
DAG-level orchestration inside the data pipeline
- DAG-level task orchestration within data pipelines
- Python operators, sensors, and task dependencies
- Execution graph for jobs that run inside your pipeline
- Manages retries within a single DAG context
control-m adds
The coordination layer around your DAGs
- Coordination layer around DAGs — triggers Airflow based on upstream conditions: file arrivals, API events, other tool completions
- Tracks each DAG’s SLA contribution across the full end-to-end workflow, not just its own routine
- Manages failure recovery when upstream dependencies fail before Airflow even starts
- Existing DAGs don’t need to be rewritten or migrated
MONITOR INFRASTRUCTURE
Monitor GCP Managed Instance Group jobs from one place
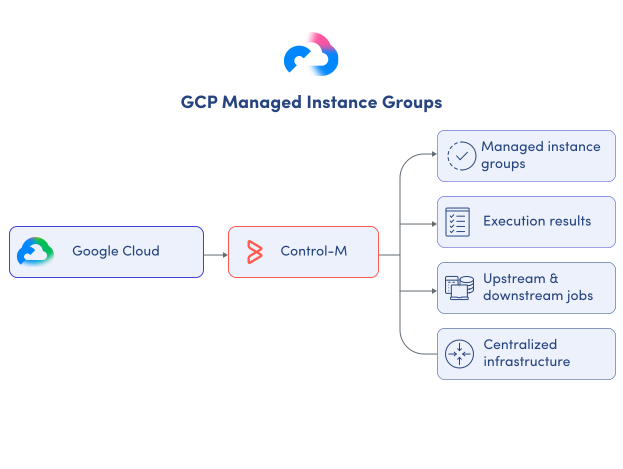
Google Cloud provides infrastructure-level status, but that alone doesn't show how instance group operations affect dependent enterprise workflows. Control-M centralizes job execution visibility across platforms, giving DevOps and SRE teams access to:
-
Managed Instance Groups job status
-
Execution results and job output
-
Upstream and downstream job dependencies
-
Job duration and execution history
-
Centralized infrastructure workflow monitoring
SLA ASSURANCE
Keep GCP Managed Instance Group maintenance workflows on schedule
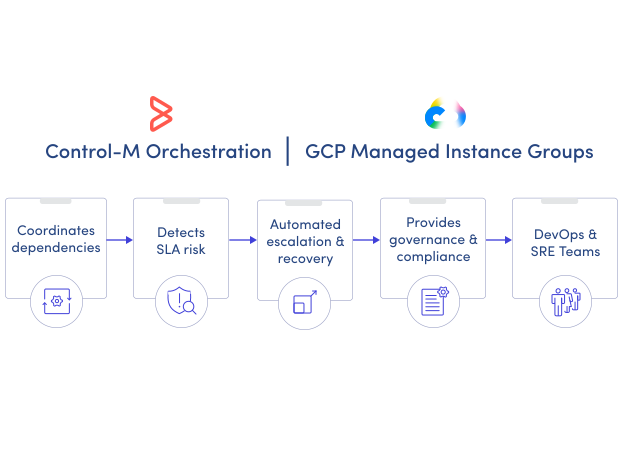
Google Cloud manages infrastructure operations but doesn't track business deadlines across external systems. Control-M connects Managed Instance Groups jobs to end-to-end SLA management, helping platform teams identify delays, coordinate recovery, and protect critical service handoffs through:
-
Configurable workflow SLA deadlines
-
SLA monitoring and breach prediction
-
Upstream dependency failure visibility
-
Automated job retries and reruns
-
Coordinated downstream execution control
Documentation
Bring order to complex workflows
Learn how Control-M helps teams orchestrate complex processes with greater visibility, coordination, and control.
